Websites & Conversion
WordPress for clinics: test your booking journey after every update
A clinic-specific update checklist covering recoverable backups, staging, mobile booking, consent choices, payment testing and proof that reception receives each enquiry.
The short answer: test the whole journey, not just the homepage
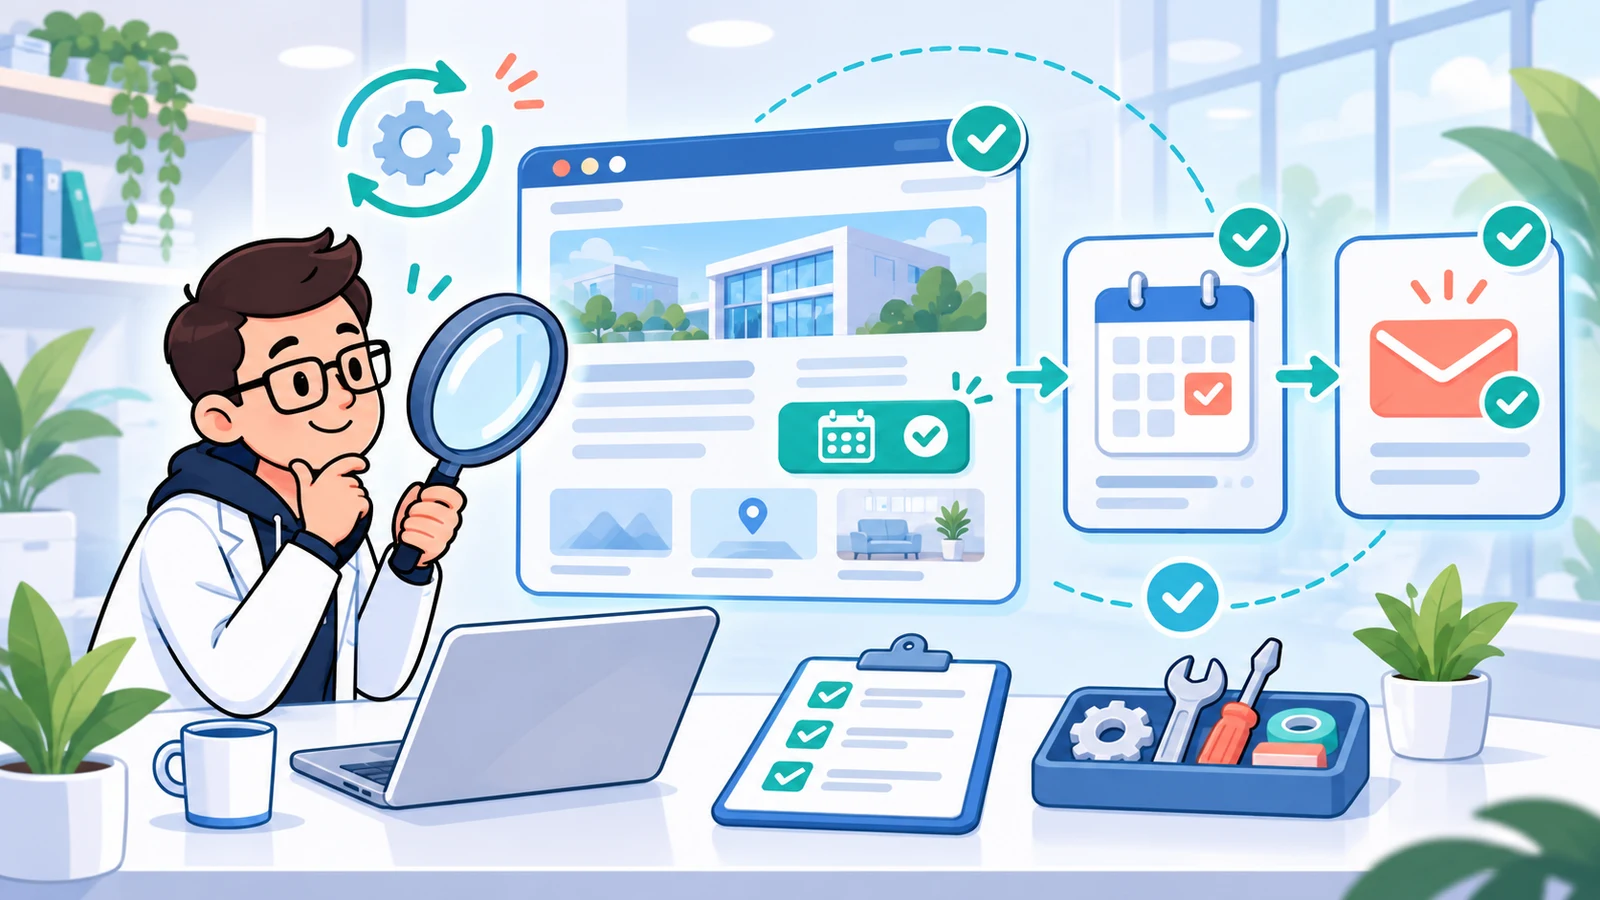
After a WordPress update, follow a clinic enquiry from the original page to its actual destination. Check mobile links, form errors, privacy choices, booking availability and confirmation messages, then ask reception to verify receipt. A working homepage and a green submission message do not prove that anyone can act on the enquiry.
Make this a repeatable release check owned jointly by your website maintainer and clinic manager. The maintainer checks the technical delivery; reception confirms the operational result. This guide focuses on that handover, using official guidance checked on 6 November 2026, rather than offering a general security audit.
Five quick checks before you sign off an update
Start with this short acceptance test, then use the detailed checks below for the parts affected by the update. Run disruptive failures and payment simulations in staging, not against a live patient journey.
- Open a service page on a logged-out phone browser and follow its main booking action to the correct branch.
- Trigger a required-field error, correct it and confirm that the form remains usable.
- Send an authorised synthetic request and ask reception to find its test reference in the working queue.
- Repeat the route with optional tracking rejected; check the alternative contact route if an embed cannot load.
- Record the result, software versions and responsible maintainer, including any unresolved failure.
Write down what a successful booking means
Start with the routes people actually use: a service page, a branch page, a persistent booking button and the contact page. Record where each route ends. Some clinics offer an appointment request; others let visitors reserve a live slot. Those are different outcomes and need different confirmation wording.
For a request, success means that the correct team receives a usable record and the visitor understands what happens next. For an instant booking, verify the appointment in the authoritative booking system, including location, practitioner where relevant, time and payment status. Do not label an unreviewed request as a confirmed appointment.
Keep the test script short enough to repeat. Include a reference for each test, the expected destination, the person checking it and the result. A dated record with no patient information is more useful than an informal message saying the site looks fine.
Include the ordinary out-of-hours route in that script. Confirm that an acknowledgement accurately describes the clinic's staffed hours and does not promise a callback the team cannot provide. If the form serves several branches, nominate someone to verify each destination instead of assuming one successful submission proves every routing rule works.
Prepare a recoverable backup and a controlled staging site
WordPress recommends backing up before updating. Ask your maintainer to confirm that the backup covers both files and the database, when it completed, where it is stored and who can restore it. A scheduled backup notification is not evidence that restoration has been tested.
Use a staging environment for changes that affect forms, booking embeds, payments, caching or consent management. Protect it with access controls, keep it out of search indexing and use synthetic records. Do not casually copy a live database containing patient enquiries into a less protected testing environment.
Disable outbound patient messages and real payment activity in staging. Check which external connections remain active: a copied website can still send to a live reception inbox or modify a real calendar. Give test integrations distinct credentials and destinations where the provider supports them.
Agree recovery authority before deployment. Restoring a database can overwrite enquiries received after the backup, so the maintainer needs a reconciliation plan. If rollback would reintroduce a security vulnerability, escalate containment and repair rather than reopening the vulnerable service automatically.
Test as a visitor on a phone
Use a logged-out browser and a real phone as well as desktop checks. Administrator sessions often bypass caching. After deployment, have the maintainer clear the relevant site and CDN caches, then verify the public version. Otherwise an old cached page can conceal a broken update or make a successful fix appear ineffective.
Follow the primary button, telephone link and any external booking link. Confirm the correct branch and service remain selected. Check that a sticky banner, chat panel or cookie notice does not cover the final action when the keyboard opens.
Increase text size, rotate the phone and use keyboard navigation on desktop. Check visible focus, readable field labels and whether the booking widget remains usable. Record the device and browser for failures; a screenshot alone rarely explains the sequence that caused them.
Make forms fail clearly and succeed honestly
Submit once with a required field missing and once with an invalid email format. The page should identify the problem, explain how to correct it and preserve other appropriate entries. W3C guidance emphasises clear feedback for both errors and successful submissions, including feedback accessible to assistive technology.
Then use an approved test identity and a clinic-controlled email address. Avoid real symptoms, medical histories or photographs. Check the visitor's acknowledgement, the reception record and any integration queue separately. A message accepted by an email service has not necessarily arrived in the team's working inbox.
Test the failure route in staging with your maintainer. If an integration is unavailable, the site should not imply that an appointment is confirmed. Agree how staff discover failures and recover legitimate requests without encouraging visitors to send sensitive details through an insecure alternative.
Exercise every consent path without weakening privacy
Run the journey with optional technologies rejected, accepted and subsequently withdrawn. Confirm that the stored choice is respected when the visitor changes pages or returns. Ask the maintainer to inspect actual network activity, not just whether the banner disappears.
ICO guidance requires prior consent for storage and access technologies unless an applicable exception is met. Its updated guidance includes exceptions with specific conditions; do not assume a tool is exempt simply because its supplier calls it essential or privacy-friendly. Have the clinic's responsible adviser check the implemented purposes.
If a booking embed fails when optional tracking is refused, investigate its configuration and provide an appropriate alternative booking route. Do not solve the problem by silently accepting tracking, hiding the refusal control or removing privacy information. Keep any marketing opt-in separate from the administrative enquiry.
Check payment outcomes in the provider's test environment
Where a consultation requires a deposit or payment, test success, decline, cancellation and any additional authentication step using the payment provider's documented sandbox or test mode. Stripe, for example, provides simulated payment details and says not to test in live mode using real payment details. Follow your own provider's instructions.
Verify the relationship between payment and appointment status. A declined transaction must not appear paid; a successful test payment must reach the correct test booking record. Ask the maintainer to check delayed or repeated provider notifications so the same event does not create duplicate appointments.
Before release, confirm the intended production configuration without making an unauthorised live charge. Keep test credentials and test slots out of the public journey. Production verification must follow the provider's supported procedure, with any limitations recorded rather than concealed.
Keep verification evidence out of marketing analytics
Google warns that URLs, page titles, form inputs and event fields can inadvertently send personally identifiable information to Analytics. Inspect what leaves the browser after an update, especially if a form or booking plugin has changed its redirect address.
Do not send patient details, health information, appointment identifiers or free-text enquiries to marketing analytics. Keep delivery checks inside approved operational systems. Use non-identifying test references and restricted technical evidence; a screenshot containing a reception inbox should not become an attachment in a general marketing report.
Hypothetical example: the form works but reception sees nothing
Imagine a fictional two-branch clinic updating its form plugin. A test visitor sees a success message, but the branch coordinator cannot find the enquiry. The maintainer traces the synthetic submission and discovers that the notification destination has reverted to an old administrative address.
The team corrects the routing, repeats the test for both branches and confirms receipt in each working queue. It also checks whether genuine enquiries arrived during the affected period using authorised records. This is an illustrative failure scenario, not a real client result or a claim about any particular plugin.
The release checklist reception can sign off
Use the same checklist after relevant core, theme and plugin updates, including automatically deployed changes. Prioritise checks according to the change, but always verify the main enquiry route. Record unresolved issues, an owner and the decision about whether the affected route can remain available.
After deployment, agree a short observation window with reception and the maintainer. Compare incoming requests with the approved system's delivery records, looking for failures, duplicates or unexpected routing. Investigate anomalies within those protected systems. A quiet inbox alone cannot distinguish a technical fault from a day with fewer enquiries, so combine staff observations with actual delivery evidence.
- Backup completion and recovery responsibility are recorded; staging uses controlled test data.
- Mobile and desktop links reach the correct service and branch without overlays blocking controls.
- Invalid entries produce useful errors; successful requests receive accurate acknowledgement wording.
- Reception confirms the test record reached the intended queue and can be actioned.
- Consent rejection, acceptance and withdrawal behave as approved, without bypasses.
- Payment outcomes and booking status agree in the provider's supported test environment.
- Patient information is absent from analytics requests and shared test evidence.
- Test records and temporary slots are removed through the agreed process; production checks are logged.
FAQ: Should we switch off automatic updates?
Not as a blanket response. Agree an update policy with your maintainer that balances timely security fixes with compatibility checks and monitoring. Automated updates still need an accountable owner, alerts and a booking test. Higher-risk changes may need a more controlled deployment process.
FAQ: Is a successful test email enough?
No. Confirm the message or record reached the correct working destination, contains usable administrative information and has someone responsible for responding. Check the visitor's acknowledgement separately. If the clinic uses a booking platform, verify its actual appointment status rather than relying on email alone.
FAQ: How often should we repeat the full test?
Repeat it after changes affecting the journey and at an agreed routine interval, since external booking services can change independently of WordPress. Use incident history and business risk to set the schedule. There is no universal frequency that guarantees a functioning booking system.
Turn the checklist into a maintenance requirement
Ask your website partner to include booking verification and reception sign-off in the maintenance scope. Marketing.clinic can help review the route, responsibilities and evidence required. Bring your website address and a description of the booking setup, not patient records or passwords, to the first conversation.
Need help putting this into practice?
Talk to our team about your website, enquiry journey and the practical changes your business needs. We can help define the next step and who should own it.
Get expert website advice